IA-06
Process Understanding and Control Assessment Kit (RCM)
Understand and document the process, then build the risk and control matrix and the audit program.
IA-08
Review IT and cybersecurity controls with templates referenced to the NCA Essential Cybersecurity Controls (ECC).
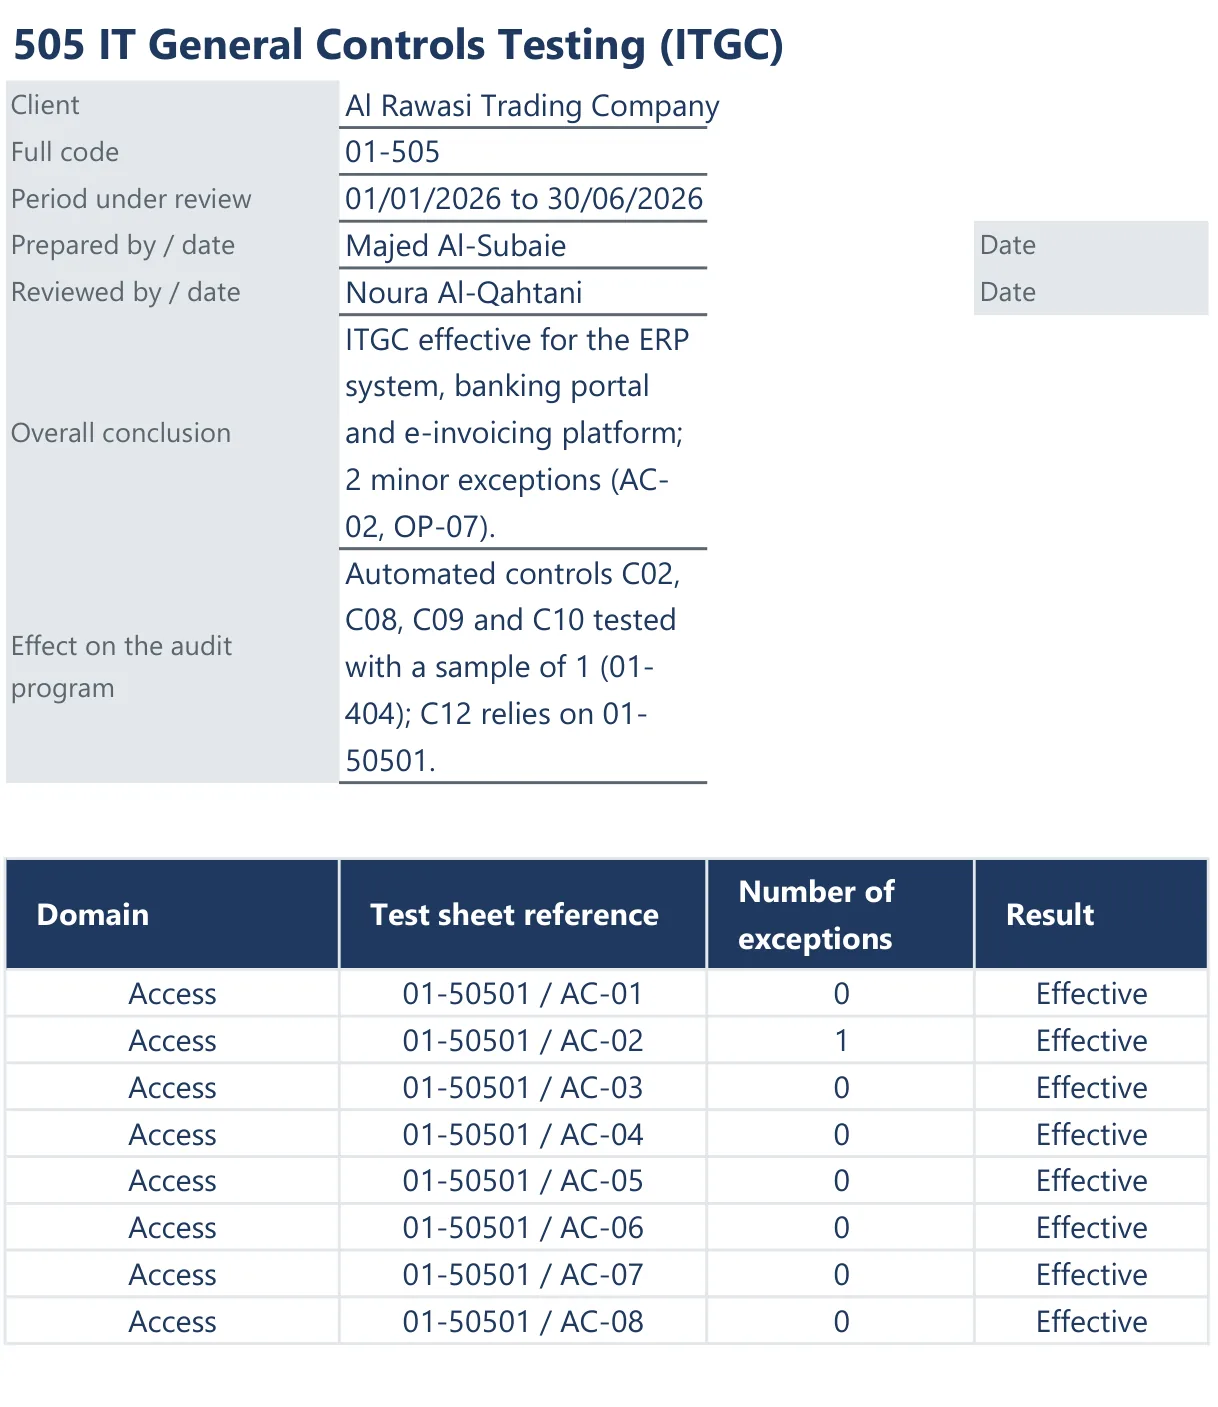
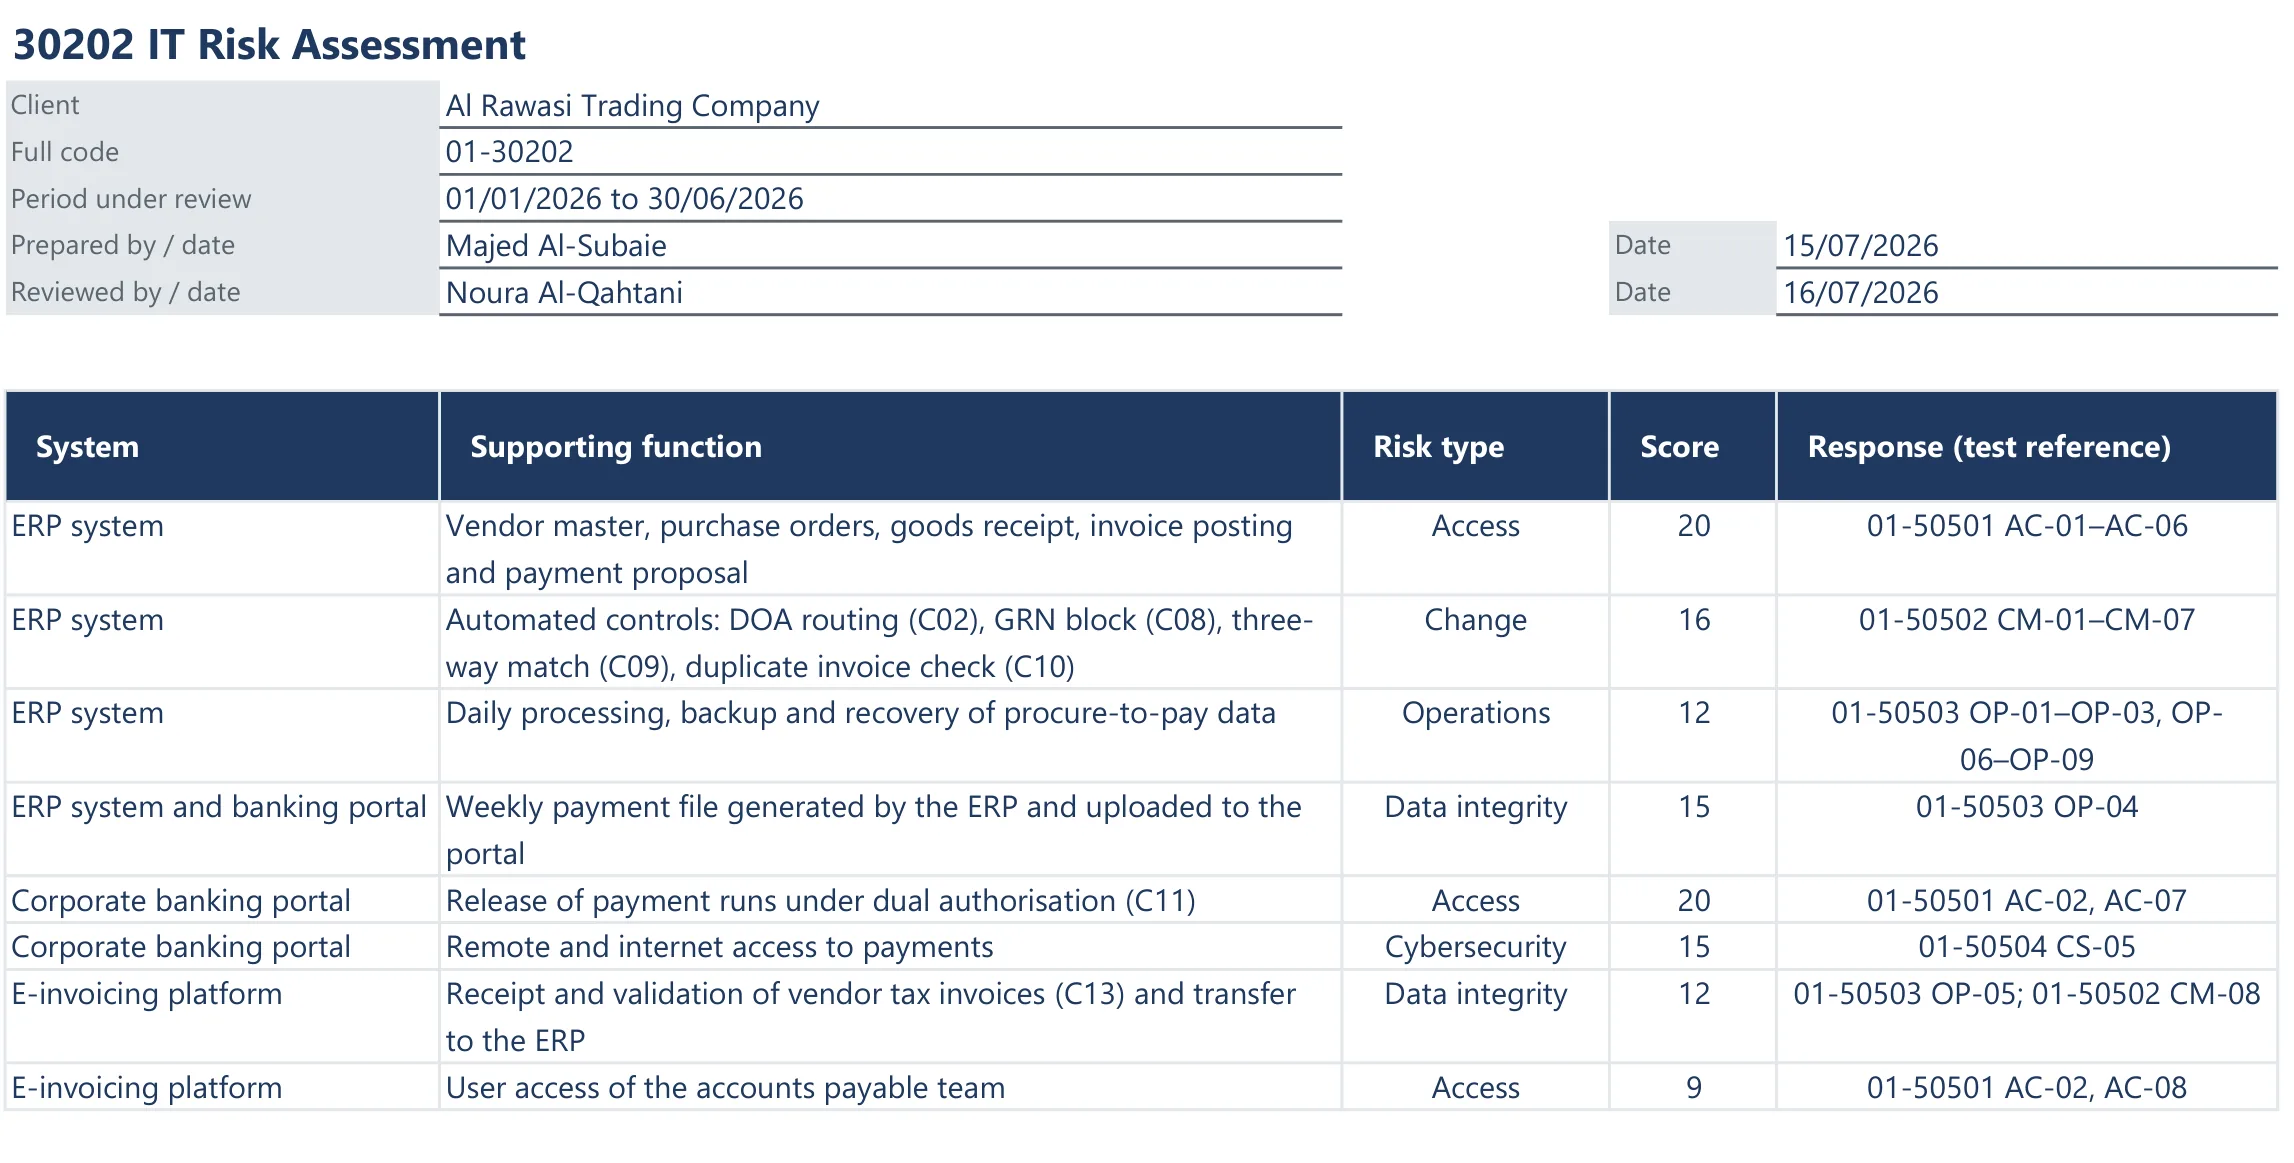
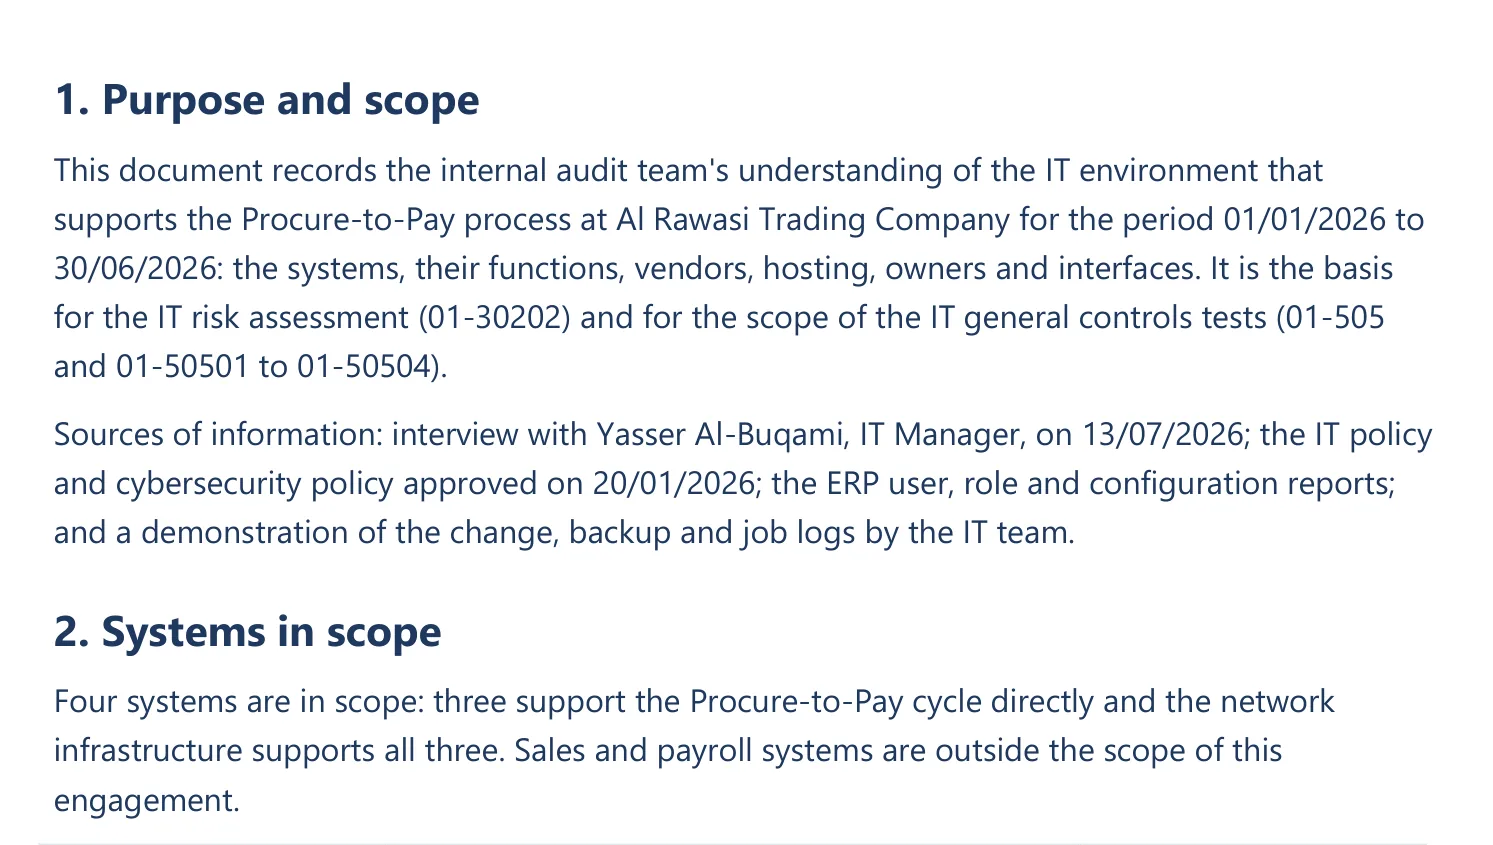
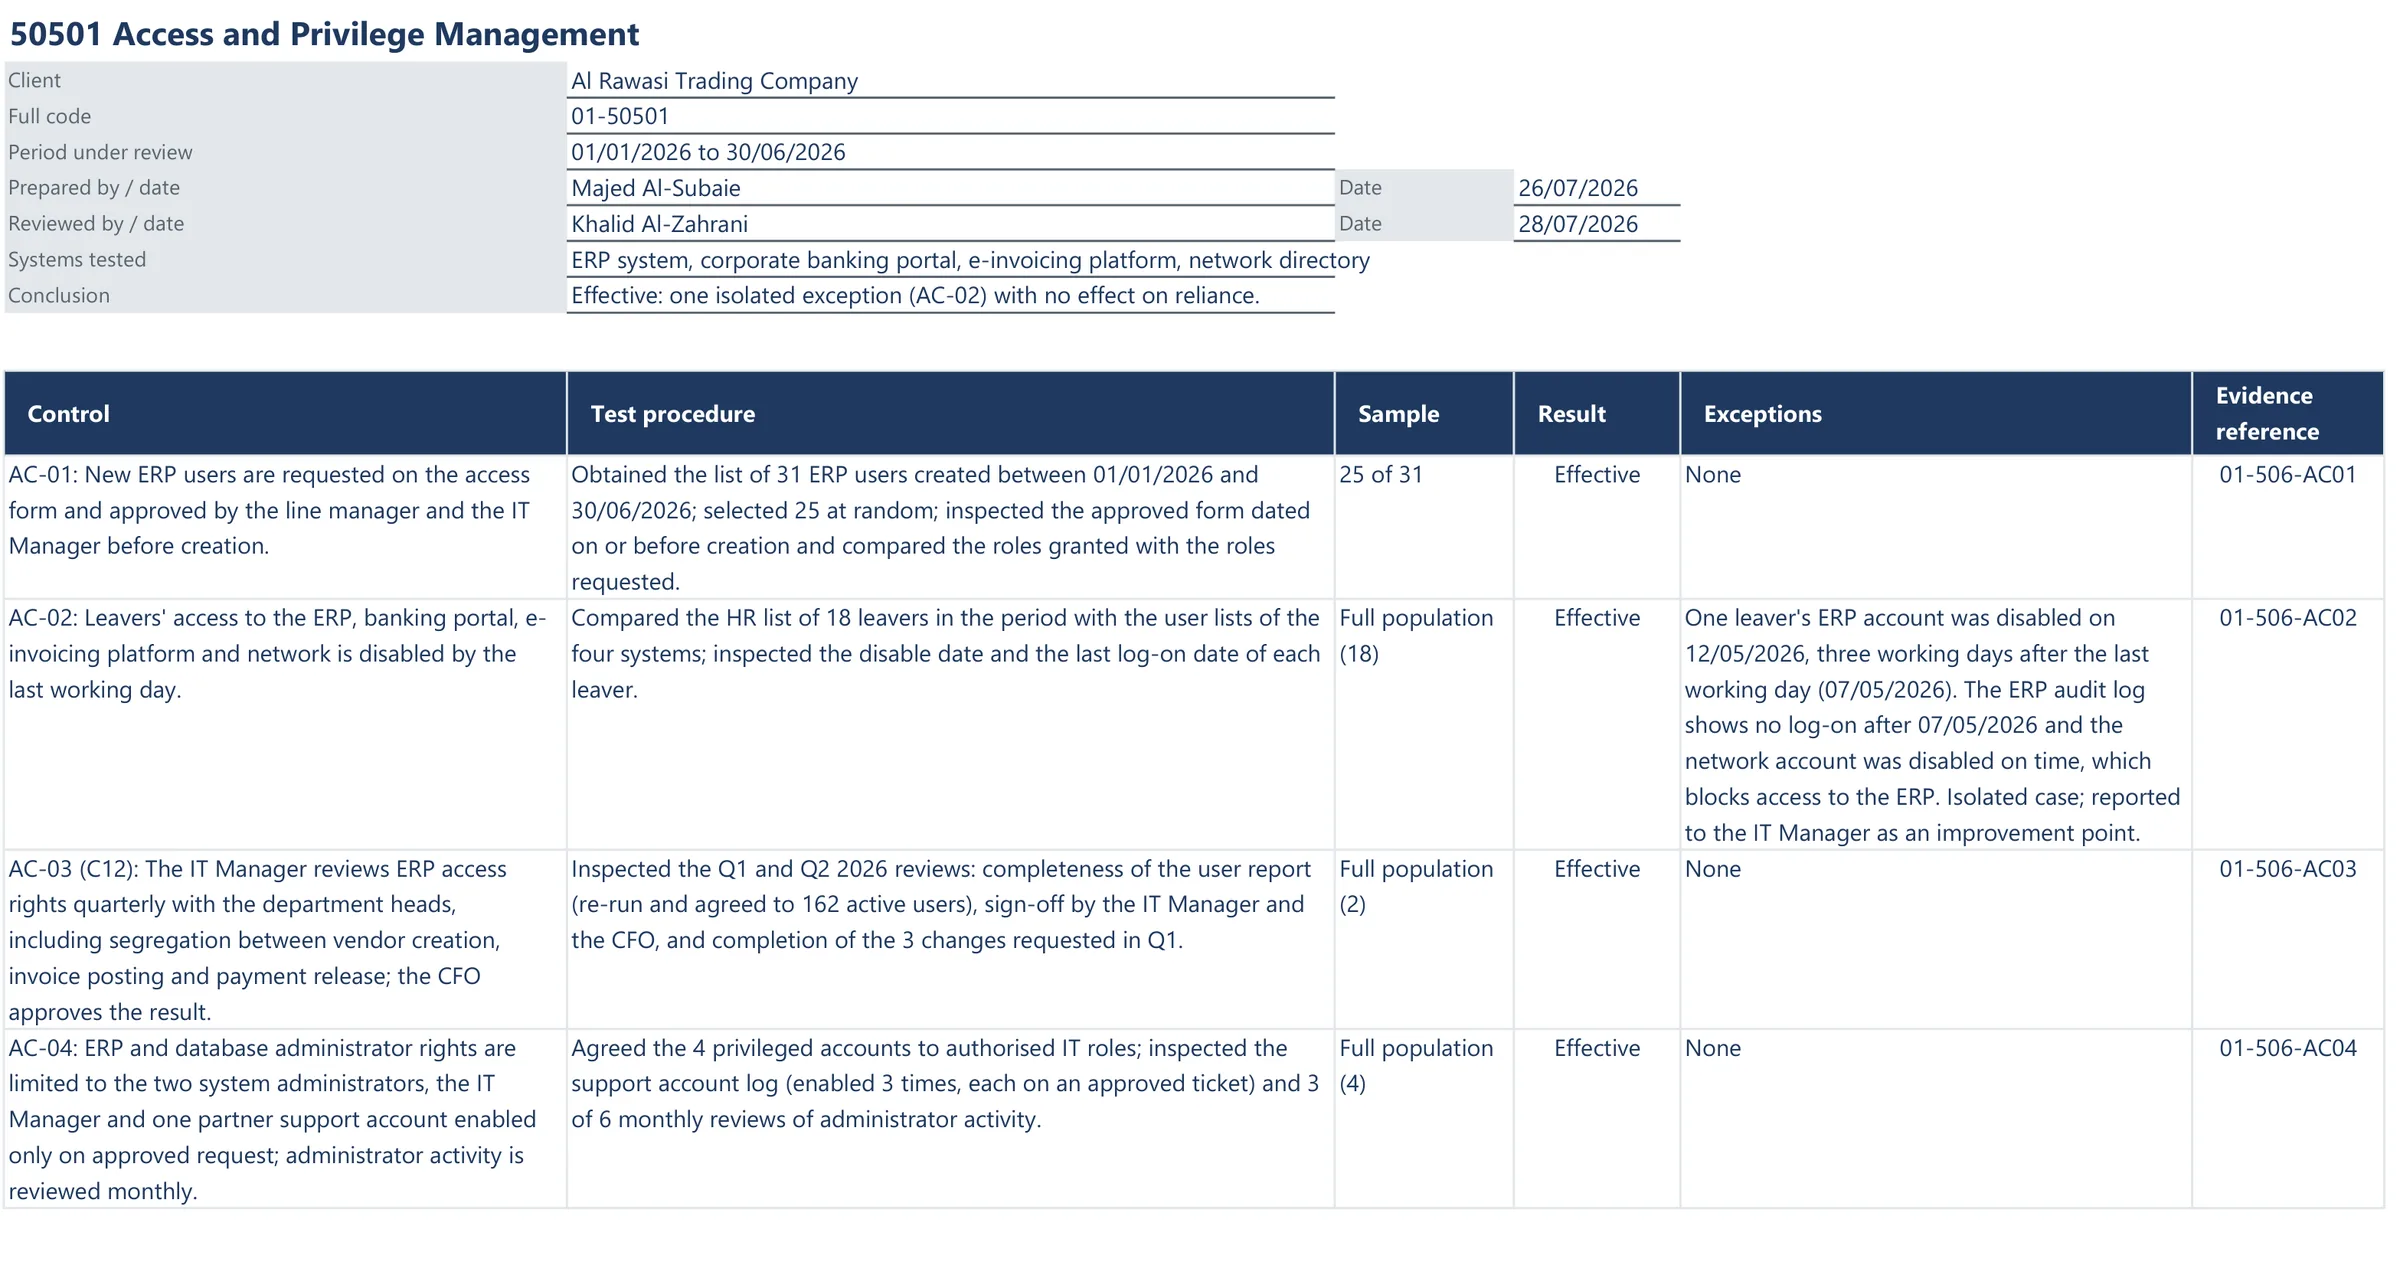
The systems behind a business process are often left out of scope, or tested with a generic checklist unrelated to risk. This kit starts with the IT environment in 406: the systems, applications and databases that support the process, and who is responsible for them. 30202 then assesses access, change and data integrity risks. 505 organises ITGC testing in four areas: access and privilege management, including segregation of duties (50501); system change management (50502); IT operations, backup and recovery (50503); and cybersecurity and data protection (50504), tested against the NCA ECC and the PDPL.
Audit firms and in-house internal audit departments whose engagements cover IT-dependent processes, from planning and process understanding through to testing.
| Code | Paper | Format | What you get | Reference |
|---|---|---|---|---|
| 30202 | IT Risk AssessmentReference: 13.2 | Excel | Template + worked exampleTemplate + example | 13.2 |
| 406 | IT Environment UnderstandingReference: 9.1, 14.1 | Word | Template + worked exampleTemplate + example | 9.1, 14.1 |
| 505 | IT General Controls Testing (ITGC)Reference: 14.2 | Excel | Template + worked exampleTemplate + example | 14.2 |
| 50501 | Access and Privilege ManagementReference: 14.2 | Excel | Template + worked exampleTemplate + example | 14.2 |
| 50502 | System Change ManagementReference: 14.2 | Excel | Template + worked exampleTemplate + example | 14.2 |
| 50503 | IT Operations and BackupReference: 14.2 | Excel | Template + worked exampleTemplate + example | 14.2 |
| 50504 | Cybersecurity and Data ProtectionReference: 14.2 | Excel | Template + worked exampleTemplate + example | 14.2 |
Every kit also includes a user guide (PDF and PowerPoint) and the licence terms, in Arabic and English.
IIA Global Internal Audit Standards (2024) references, with ISQM 1 and SAMA principles where they apply, as given in the guide. References are for cross-referencing and do not imply IIA endorsement.
IA-06
Understand and document the process, then build the risk and control matrix and the audit program.